Cybersecurity leadership and compliance
Fractional CISO services, ISO/IEC 27001 and ENS implementation, and business continuity for organisations that need a security lead without hiring one full-time.
When a fractional CISO is the right call
Most organisations don’t need an in-house security department. They do need someone accountable for security: setting direction, prioritising the work and reporting to the board.
A client or tender requires ISO 27001 or ENS
Deadlines are fixed, and you need to reach the audit with a system that actually runs.
No one formally owns security
Security decisions are made without a risk assessment or anyone accountable for them.
Your IT provider keeps systems running, but no one manages risk
ShieldAudit works alongside your in-house team or IT provider and adds the security governance that’s missing.
You’ve had a security incident
Understand what happened, contain it, recover and fix the root cause.
Services
Security governance, compliance and hands-on implementation.
Fractional CISO (vCISO)
Part-time security leadership: strategy, risk, budget and board reporting, without a full-time executive hire.
Learn moreISO/IEC 27001
ISMS implementation and certification readiness: scope, risk assessment, Statement of Applicability, policy direction and sign-off, and internal audit.
Learn moreENS (Spanish National Security Framework)
Compliance with Spain’s Esquema Nacional de Seguridad (Royal Decree 311/2022) for public bodies and their suppliers: categorisation, controls and audit preparation.
Learn moreBusiness continuity and incident response
Business continuity plan, recovery plans with defined RTOs, an incident management procedure and regular exercises.
Learn moreControl implementation and verification
Controls are implemented and verified, not just recommended: identity and access, data protection, endpoint and cloud security.
Learn moreAlongside your IT team or provider
ShieldAudit brings security leadership (priorities, criteria and verification) without duplicating roles or replacing whoever already runs your systems.
From first call to ongoing oversight
Initial call
30 minutes to understand your context, obligations and priorities. No commitment.
Assessment
Current state and risk analysis, with an executive report for leadership.
Plan and delivery
A roadmap prioritised by business impact, and delivery of the agreed measures.
Ongoing oversight
Regular reviews, KPIs and board reporting so standards don’t slip over time.
Selected engagements
Clients are not named, for confidentiality.
Fractional CISO and ISO/IEC 27001 certification
Acting CISO, leading the organisation’s information security programme.
- Leadership of the security programme and the ISMS
- Support through to ISO/IEC 27001 certification
- Business continuity plan with five recovery plans and an annual exercise schedule
- Security KPIs and regular reporting to management
Head of Cybersecurity and ISO/IEC 27001 certification
Head of cybersecurity at an energy company.
- Led the cybersecurity function, reporting to executive management
- ISMS implementation as head of security
- ISO/IEC 27001 certification project through to certification
Working model
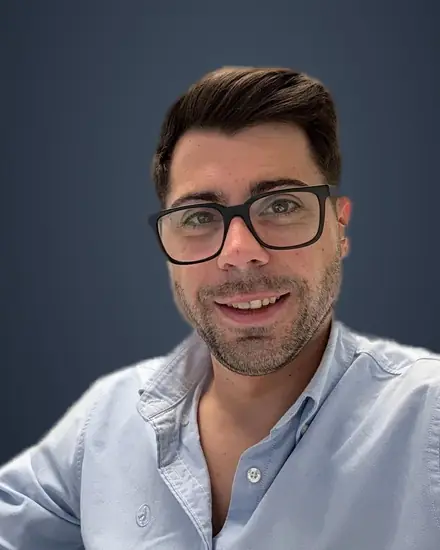
ShieldAudit is an independent consultancy. One senior consultant, Javier Moreno, owns the engagement from assessment to ongoing oversight.
One point of contact
The same person assesses, delivers and follows up.
Priorities driven by business impact
Every recommendation is justified by the risk it reduces and what it costs.
Implementation and verification
The work includes putting controls in place and checking they work, not just recommending them.
English and Spanish
Meetings and deliverables in either language, or bilingual if your organisation needs it.
What clients say
Muy buena experiencia con Shieldaudit. Javier es un auténtico profesional, cercano y siempre dispuesto a ayudarte en todo lo que necesites. Se nota que sabe lo que hace y que le importa hacer las cosas bien. Me gustó mucho la claridad con la que explica todo y la tranquilidad que transmite durante el proceso. Da gusto trabajar con gente así, que combina profesionalidad con trato humano. Sin duda, totalmente recomendable.Contacté con Shieldaudit para realizar una auditoría sobre la ciberseguridad de mi empresa. Javier me realizó la auditoría y, desde el primer momento, el trato fue cercano y muy profesional. Se agradece especialmente la forma en la que explican los aspectos técnicos, utilizan un lenguaje sin tecnicismos innecesarios. Cumplieron rigurosamente con los plazos acordados. Recomiendo sus servicios a cualquier empresa que busque una auditoría de ciberseguridad bien hecha.Muy satisfecho con los servicios prestados donde eficacia y profesionalidad van de la mano. A todo ello se le suma la calidad humana y buen trato de Javier. Calidad precio me atrevería a decir que son los mejores. 100% recomendable.Book an initial call
30 minutes to understand your organisation’s context and see how I can help.